The software supply chain has never been more exposed — and the organizations building on top of open source are only beginning to understand why. For decades, enterprises have treated open source packages as effectively free infrastructure, pulling dependencies into production without meaningful validation of who wrote them, how they were maintained, or whether the underlying contributors had any capacity to respond to emerging vulnerabilities. That assumption is now colliding with two accelerating forces: the machine-speed proliferation of AI-generated code and a persistent, structural underfunding of the maintainers who sit at the center of it all.
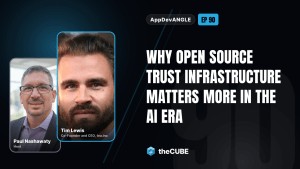
In this episode of AppDevANGLE, I spoke with Timothy Lewis, Co-Founder and CEO at tea.inc, about the intersection of open source security, software provenance, and the incentive failures that have left critical infrastructure chronically under-resourced. Lewis brings four decades of engineering experience, deep roots in cryptography, and firsthand exposure to how well-intentioned developer tooling can inadvertently amplify supply chain risk.
Our conversation explored several interconnected themes: how AI at the execution layer is changing the risk profile of open source package ecosystems; why maintainer overload has become a structural supply chain vulnerability; what enterprise-grade provenance and identity validation actually require; and why the market has consistently over-invested in code generation while under-investing in the review, governance, and trust infrastructure that makes generated code safe to ship.
The broader signal is this: the open source security problem is no longer a community governance issue. It is an enterprise infrastructure risk that demands the same investment rigor as any other critical dependency.
AI-Generated Contributions Are Turning Package Maintainers Into a DDoS Target
The most immediate effect of AI at the execution layer is volume. Pull requests that once arrived from known contributors after days of back-and-forth community engagement are now arriving from unknown sources in bulk, with no relationship history and no shared understanding of a project’s direction. The review burden has shifted from manageable to unsustainable for many maintainers.
Lewis framed it precisely: “…some of the contributions may be valid, [but] understanding where the North Star is for the project, it still takes a lot of time, and now it takes a lot more time for the maintainers to actually review.” A DDoS attack doesn’t need to compromise a system to take it down; it just needs to overwhelm its capacity to respond. The same dynamic is playing out in open source governance, where contribution volume is outpacing the human capital available to evaluate it.
The downstream consequence is not just slower merge times. When maintainers become overwhelmed, security reviews get skipped, packages get abandoned, and the organizations that depend on those packages keep shipping into production without knowing the underlying project has effectively gone dark. The Ingress-NGINX deprecation, referenced by Lewis, is a visible example of an infrastructure component reaching end-of-life while enterprises were still actively building on it.
The pattern here is structural, not incidental. Open source maintainers are operating critical infrastructure for global enterprises on voluntary or minimally compensated terms, and AI tooling is now adding inference costs on top of the time costs they were already absorbing.
Provenance Is the Missing Foundation of Software Trust
The deeper problem beneath maintainer overload is provenance. Enterprises cannot make informed trust decisions about packages they cannot trace. And right now, the industry’s ability to trace software to its origin remains profoundly weak.
Lewis noted that at the time tea.inc. began focusing on this problem, only six to seven percent of open source software was cryptographically signed. The implication is stark: the vast majority of packages in enterprise dependency trees carry no verifiable attestation of their origin. “Six to seven percent of all software was signed in open source, and now it’s like, hey, no longer is it a nice to have; now it’s a need to have.”
The problem compounds across version control system migrations and common development practices. As Lewis explained, squash merges — a widely adopted workflow in GitHub-based development — do not preserve commit signature history. That means even when signatures exist, the evidence chain breaks across normal development operations. What the industry needs, Lewis argued, is not just better signing tooling but validated historical indexes of signatures across repositories: “I think it’s just a big evidence indexing problem that needs to occur, and then having and controlling and holding and validating that evidence is an expensive process that people need to contribute to in order to make it work.”
This distinction matters because it reframes the problem. Provenance is not a feature that can be added to existing package managers. It requires a persistent, auditable, cryptographically anchored record infrastructure, which does not currently exist at scale.
Governance Adoption Is Lagging Dangerously Behind Threat Exposure
Despite growing awareness of supply chain risk, enterprise governance response has been slow. Lewis observed that many organizations still rely on package manager maintainers to enforce security gates. This delegation of responsibility is becoming more and more inadequate given maintainer capacity constraints. Meanwhile, the policies that do exist within enterprises often live at the team level rather than the ecosystem level, creating inconsistent coverage across dependency trees.
The gap between security rhetoric and security behavior is real. As Lewis put it: “The enterprises, the good ones, adopt their own policies and get through this. And the ones that are lagging behind, still lag behind.” That bifurcation is becoming a competitive and operational liability, particularly as regulators begin to move.
Lewis pointed to NIST requirements around provenance validation as a potential forcing function. The question is whether those requirements will be elevated into enforceable penalties or remain aspirational guidance. Until regulatory pressure becomes consequential, the economic logic for many organizations will continue to favor shipping fast over validating deeply.
The Incentive Gap Is the Security Gap
The core structural failure in open source security is not technical; it is economic. The tools to cryptographically sign packages, validate provenance, and enforce governance policies exist. They are clunky, inconsistently adopted, and require effort to implement, but the primitives are there. What has been missing is a viable mechanism to compensate the people responsible for doing that work.
Lewis was direct about the nature of the failure: “The cost isn’t just your time, which was already running thin. But now the cost is time, plus inference.” AI-assisted review is the most scalable path to managing increased pull request volumes, but it carries real compute costs. Maintainers who were already operating at the edge of their capacity without financial support now face an additional category of expenditure with no clear funding source.
Current mechanisms for directing commercial value back to open source maintainers are fragmented and unreliable at enterprise scale. What the ecosystem lacks is a structured, programmable way for enterprises that derive value from open source dependencies to direct capital back to the maintainers and contributors responsible for keeping those dependencies secure. Building that payment infrastructure is as much a part of solving the supply chain problem as building better signing tooling.
Enterprises Are Shipping Into a Trust Model They Cannot See
Perhaps the most consequential implication of this conversation is what enterprises do not know about the software they are shipping. Dependency trees are deep, provenance data is sparse, and the governance tooling that does exist tends to generate alerts rather than actionable evidence. Lewis described the current state as one where developers “don’t see where they are in their downstream dependencies in a very easy method at this point.”
The market has invested heavily in tools that help developers write code faster. It has invested far less in the infrastructure that would allow those developers, or their security teams, to understand what that code is built on and whether it can be trusted. Lewis framed this as a mismatch that the industry needs to correct: building APIs and indexing services that enterprises can use to validate the provenance and health of the packages they depend on, at the scale those dependency trees actually require.
Analyst Take
The software supply chain security problem is entering a new phase that is defined less by the sophistication of individual attacks and more by the structural inability of the ecosystem’s trust infrastructure to scale with the volume and velocity of modern development. AI-generated code is accelerating that mismatch. When machines can produce pull requests, propose dependencies, and publish packages faster than human reviewers can evaluate them, the bottlenecks that held the system together stop functioning as quality gates and become attack surfaces.
Traditional approaches such as CVE scanning, alert dashboards, and periodic governance reviews are insufficient responses to this environment. They address symptoms rather than the underlying failure: the absence of a reliable, cryptographically grounded provenance layer that allows enterprises to know, with confidence, what they are running and who is responsible for it. Building that layer requires investment in indexing infrastructure, signing adoption, and maintainer incentive models that the market has not yet prioritized at the necessary scale.
The risks ahead are not symmetric. Enterprises that establish strong provenance policies, fund their critical open source dependencies, and build governance into their pipelines will gain a durable security advantage. Those that continue to treat open source as costless infrastructure will carry compounding exposure as AI increases both the volume of code entering their stacks and the difficulty of tracing its origin.
The bigger idea is that open source is not free, and it never was. It was subsidized by the time and effort of maintainers who built it out of conviction. The bill for that subsidy is now coming due, and enterprises that fail to recognize open source maintainers as critical infrastructure dependencies will find themselves building on foundations they cannot inspect, cannot verify, and cannot trust.