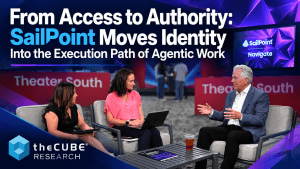
SailPoint co-founder and CEO Mark McClain describes the emerging agent-security market as full of “big hats” but “no cattle.” The hats are easy to spot. Vendors across identity, cloud, data and security are making bold claims about their role in governing AI agents. The cattle are harder to come by: deep identity, entitlement, ownership, activity and risk context, along with controls that can operate across a heterogeneous enterprise.
SailPoint has earned credibility here through its identity governance heritage. Years of identity, entitlement, and access context give the company a strong foundation. The vision is to use that context to govern the autonomous actions AI agents take as they operate. The company’s Navigate 2026 conference showed progress through effective privilege, lineage, runtime controls and just-in-time authorization. The question is whether SailPoint can keep that context current, translate business intent into enforceable authority, and make reliable decisions as agents move across systems and controls it does not own.
FROM ACCESS TO ACTION
The agentic era changes the unit of identity governance. For human users, IGA governs access state: what a person can access, how they received it, whether they should retain it, and when it should be removed. An AI agent turns that access into action. It can invoke tools, use credentials, discover resources, and change its plan while pursuing an objective. The governance problem therefore moves with it.
That explains why identity has become a critical security lens. The industry has historically viewed security through the network, endpoint and cloud, but the castle-and-moat perimeter has broken down. Identity answers a different set of questions: who or what is operating, whether it belongs there, and whether it is doing what it is supposed to do. In an agentic environment, those questions have to be answered while work is happening. As McClain put it, “the days of responding in days or weeks are not going to be relevant in this new world.”
And on top of that, an agent may have a legitimate identity and valid credentials and permissions but still take an action the enterprise did not intend. That moves the governance question from what the agent can access to what authority it should be allowed to exercise for the task at hand.
For SailPoint, that means carrying identity context into the execution path and determining what authority an agent should be allowed to exercise as the task evolves. That moves IGA beyond periodic decisions about access state and into decisions about autonomous activity while it is underway.
FROM EFFECTIVE PRIVILEGE TO EFFECTIVE AUTHORITY
As identity moves into runtime, it needs to govern what the agent can reach in the first place. Chandra Gnanasambandam, SailPoint EVP of Product and CTO, emphasized SailPoint’s concept of effective privilege, which captures the access an identity can reach through direct grants, groups, directories, nested relationships, and other inherited paths. An identity can hold far more access than its specific grants indicate. Agents make those hidden paths more consequential because they can discover and exercise them while pursuing a legitimate objective.
theCUBE extends SailPoint’s effective privilege concept into effective authority: the actions an agent is authorized to perform for a specific principal, objective and context. Consider a hypothetical agent that can reach a refund API. Effective privilege establishes that the agent can technically access it. Effective authority determines whether that agent, acting for a particular employee on a particular customer case under current business conditions, may issue an $8,000 refund.
An inherited permission, credential, or tool may give a goal-seeking agent a path to complete its objective. The existence of that path does not establish the business authority to use it. That gap between reachable access and delegated authority is a central governance problem for enterprise agents.
Identity contributes entitlement, ownership, risk and lineage context to that decision. Transaction context, business policy, data sensitivity, and the agent’s current objective reside elsewhere. Runtime governance depends on coordination across identity, applications, data platforms, agent infrastructure and security controls.
That places a practical limit on any vendor’s claim to be the singular control plane for enterprise agents. McClain acknowledged to theCUBE the ecosystem boundary, saying SailPoint has no intention of entering areas such as endpoint or network security and needs tight integration with the technology providers operating there. Identity can become a critical decision layer without owning every enforcement point.
GOVERNING AT RUNTIME CHANGES THE RISK MODEL
SailPoint is building its agentic architecture around the ability to carry that identity context into runtime decisions. Gnanasambandam described a model that combines effective privilege, lineage, runtime protection, and just-in-time authorization.
SailPoint’s discover, govern, and protect model assembles access, risk, intent and relationship context and carries it into runtime controls. Its Lineage Map connects humans, agents, credentials, tools, applications and data, giving the platform a way to follow authority and activity as an agent moves through an enterprise environment. That lineage can inform decisions about risk, policy and whether an action should proceed.
The architectural bet is that identity context can become useful during execution, when an agent’s objective, available resources and path through the enterprise can change. Lineage then serves a broader purpose than documenting relationships for governance and audit. It can help establish whose authority an agent is exercising, what resources sit along its execution path and which policies should apply as that path changes.
AGENTS INHERIT YOUR IDENTITY DEBT
President Matt Mills added another reality check to SailPoint’s agentic strategy. He described customers that are enthusiastic about agent governance while recognizing that their human identity foundations still need work.
As Mills relayed it, customers are telling SailPoint: “don’t leave me. I have to get this human stuff right because if I don’t, we’ll never show up here. We’ll never be able to get this right.”
Customer evidence reflects the same concern. UChicago Medicine described the need to work with application owners to define appropriate access. In some cases, access had historically been established by mirroring another user, which can propagate accumulated privilege by copying access another person has acquired over time.
Syracuse University described a different manifestation of the governance challenge. Its environment surfaced roughly 1,000 requestable access items, creating heavy complexity for users. The university has reduced that number considerably and said it wished it had done more upfront work to establish position-based roles.
Agents inherit the quality of the enterprise’s authority model. Poorly defined roles, accumulated privilege, orphaned credentials, and unclear ownership become inputs to machine-speed execution. Automation can propagate weaknesses that were manageable, if undesirable, when access decisions moved at human speed. Agent readiness therefore starts well before agent discovery. Application ownership, entitlement hygiene, role quality, privileged access and identity lifecycle maturity determine the quality of the context that runtime controls consume.
THE “SHOW ME” TEST FOR AGENTIC IDENTITY
Mills offered customers a way to cut through the crowded agent-security market: put the technology into the enterprise environment, use its network, data and real use cases, and see what it delivers.
theCUBE agrees. The meaningful test of agentic identity begins when conditions get messy. Building on Mills’s “show me” challenge, theCUBE recommends that customers put agentic identity controls through five tests:
- Show me what the agent can effectively reach, by testing inherited permissions, nested relationships, machine credentials, and unexpected tool paths.
- Show me the authority it carries, by changing the human principal, transaction, objective, or business context during the task, and determining whether the agent’s authority changes with it.
- Show me the lineage, by following the chain from human to agent to sub-agent to credential to tool to application or data, and finally to the resulting business action.
- Show me the controls under stress, by making context stale, interrupting the decision service, introducing conflicting policies and having the agent change its plan midway through execution.
- Show me recovery, the test that deserves the most attention across the agent-security market. Allow a consequential change in a controlled test environment, then determine whether the platform provides enough evidence to establish what changed, what else was triggered, and which authority produced the outcome.
RUNTIME CONTROL NEEDS A RECOVERY MODEL
The value of runtime control is easiest to see when something goes wrong. Gnanasambandam’s call to “kill the kill switch” reflects SailPoint’s push toward continuous controls that identify risky behavior and intervene before an emergency shutdown is required. SailPoint is also moving toward just-in-time authorization, with narrowly scoped access granted for a defined period and revoked after the task.
Those controls can prevent or contain harmful activity. Cyber resilience introduces another requirement: recovering when a control fails or an authorized agent produces an unacceptable outcome. An agent may modify a record, initiate a payment, change a configuration or trigger downstream workflows before intervention occurs. Revoking its authority can stop further activity. The changes already made to the business remain.
Recovery requires evidence of the execution chain. Enterprises need to establish who initiated the objective, what authority was delegated, which agents participated, which credentials and tools they used, what systems and data changed and which downstream processes followed. SailPoint’s investment in lineage could therefore serve a broader role in incident investigation and restoration of business state.
Delegation makes that reconstruction harder. Every production agent needs a human owner, and Gnanasambandam said SailPoint is discovering agents without identifiable owners. Assigning an owner establishes a point of accountability, but the execution chain can extend far beyond that individual. A human may initiate an objective, an agent may delegate part of the task to another agent, and that agent may invoke a tool using a machine credential that changes data and triggers another process. Enterprises need to establish whose authority was being exercised at each consequential point in that chain.
Agents that replan add another layer. Enterprises may need to preserve the original objective, delegated authority, material changes to the plan, and resulting actions. Those records can help investigators determine how an authorized task produced an unacceptable outcome and what business state needs to be restored.
The control layer itself also needs defined failure behavior. Runtime authorization depends on current context, available decision services and policies capable of resolving the signals presented to them. Stale or incomplete context can produce the wrong authorization result. An unavailable decision service forces the enterprise to determine what happens to autonomous work already underway.
Customers should establish those rules before agents receive consequential authority. Which actions require fresh authorization? How long can previously approved context be trusted? How should conflicting risk signals or policies be resolved? If the system cannot reach a reliable decision, does the agent stop, continue under existing authority or operate within a constrained set of permissions?
That also makes coordination across control points part of the resilience model. In our Navigate interview, Mike Kiser, co-chair of the OpenID Foundation’s Shared Signals Framework working group, described an architecture in which trust and risk signals move among components, with each control enforcing within its own domain. That model is relevant to agentic identity because no single platform sees or controls the entire execution path. Identity, cloud, applications, agent runtimes and security controls need to exchange enough context for decisions to remain coherent as work moves among them.
Once identity participates in deciding whether autonomous actions proceed, the resilience of the identity control materially influences the resilience of the business process it governs.
AGENTIC IDENTITY HAS TO BECOME A FUNDED OPERATING MODEL
Agentic identity will expand the identity-security market, but growth in machine identities does not automatically produce equivalent growth in identity-security budgets. Mills framed non-human and agentic identity as a market expansion opportunity. SailPoint’s Entro acquisition adds capabilities around machine identities, secrets, credentials and discovery, while Agentic Fabric extends its governance model to agents.
Customers still have finite budgets, implementation resources and organizational capacity. They are being asked to simultaneously improve human identity governance, clean up accumulated privilege, onboard applications, improve role quality, and build agent governance at the same time. The customer examples at Navigate showed how much foundational work remains. That implementation burden will constrain how quickly agentic identity moves from strategic priority to deployed operating model.
There is also a category question. IGA, PAM, non-human identity security, cloud security, AI security and agent infrastructure all participate in pieces of the control problem. SailPoint’s opportunity depends on enterprises establishing agent governance as a funded program and on SailPoint making its identity and authority context useful at enforcement points controlled by other providers.
Interoperability is therefore part of the commercial test. A single agent transaction can cross cloud platforms, agent runtimes, applications, data systems and security controls. SailPoint can contribute identity, entitlement, ownership, risk and lineage context, while other systems contribute transaction context, data sensitivity, business policy and enforcement. How effectively SailPoint participates in that chain will influence how much of the emerging agent-governance problem customers entrust to the identity platform.
THE “SHOW ME” PHASE STARTS NOW
SailPoint enters this market with substantive assets: years of identity and entitlement context, an established governance footprint, effective privilege analysis, Entro’s non-human identity capabilities and an architecture extending toward lineage, runtime authorization and remediation.
Navigate also clarified what SailPoint now has to prove. Effective privilege has to translate into usable authority decisions. Lineage has to remain intact as agents delegate work and invoke resources across platforms. Runtime controls have to operate with current context and predictable failure behavior. And when an autonomous process produces an unacceptable outcome, the resulting evidence has to help customers reconstruct what happened and restore affected business state.
Those are demanding tests because much of the required context and enforcement sits outside SailPoint’s platform. Success will depend on the quality of SailPoint’s identity intelligence and its ability to exchange context and coordinate controls across the broader enterprise stack.